Cyber security for UK businesses
support@cyberxperts.ai | +44 7490 302661

Endpoint Security

Endpoint Detection and Response for UK SMEs: What EDR Actually Does.

EDR helps detect suspicious device behaviour, investigate incidents and contain threats before they spread across the business.

Endpoint Detection and Response for UK SMEs: What EDR Actually Does — illustration

01What is endpoint detection and response?

Endpoint detection and response, often called EDR, monitors laptops, desktops and servers for suspicious behaviour. Traditional antivirus focuses heavily on known malware. EDR looks for attacker techniques such as credential dumping, malicious scripts, unusual process chains, mass file modification, persistence mechanisms and attempts to disable security tools.
Pastel white laptop X shield with document/settings icons

02Why SMEs need endpoint visibility

UK SMEs often depend on a small number of devices and cloud services. If one finance laptop or server is compromised, attackers may access email, customer data, shared drives and remote access tools. EDR provides a better chance of spotting the attack before ransomware or data theft spreads.

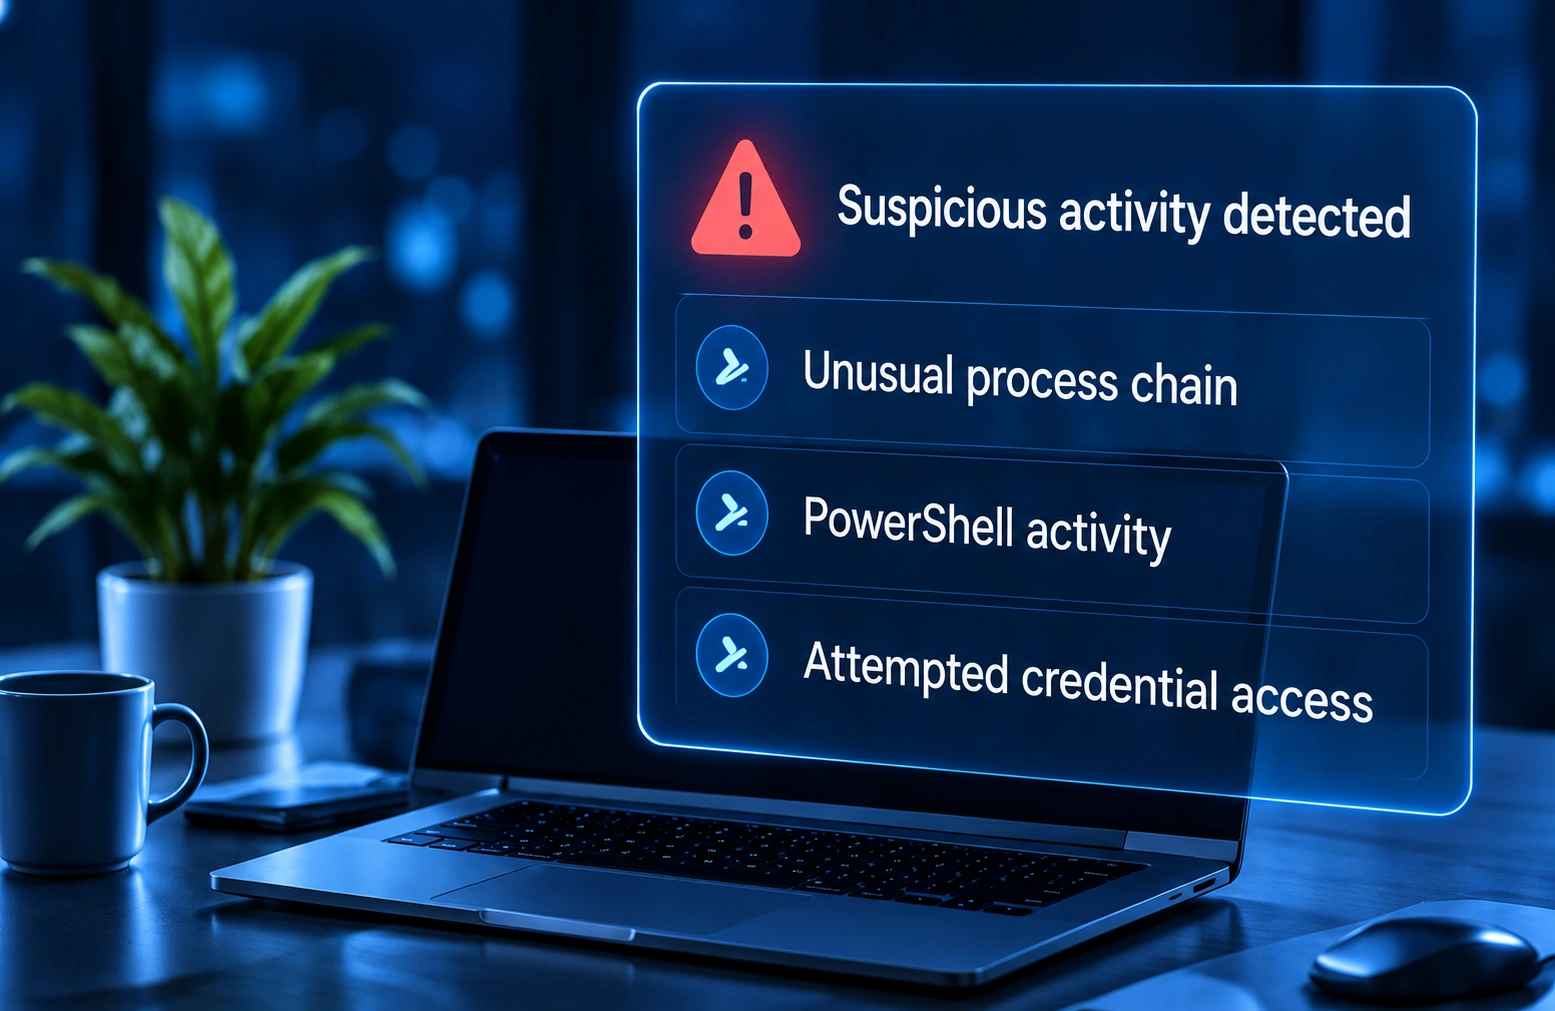
Photo of laptop with suspicious-activity alert list, plant on desk

03What EDR alerts can reveal

EDR alerts can highlight attacker behaviour that might otherwise go unnoticed. Useful alerts include suspicious PowerShell, unknown remote access tools, credential access, abnormal child processes, ransomware-like file activity, command and control connections, privilege escalation and tampering with security controls. These signals help responders build a timeline and understand attacker movement.

Suspicious PowerShell
Unknown remote access tools
Credential access
Abnormal child processes
Ransomware-like file activity
Command and control connections
Privilege escalation
Tampering with security controls

04Containment and investigation

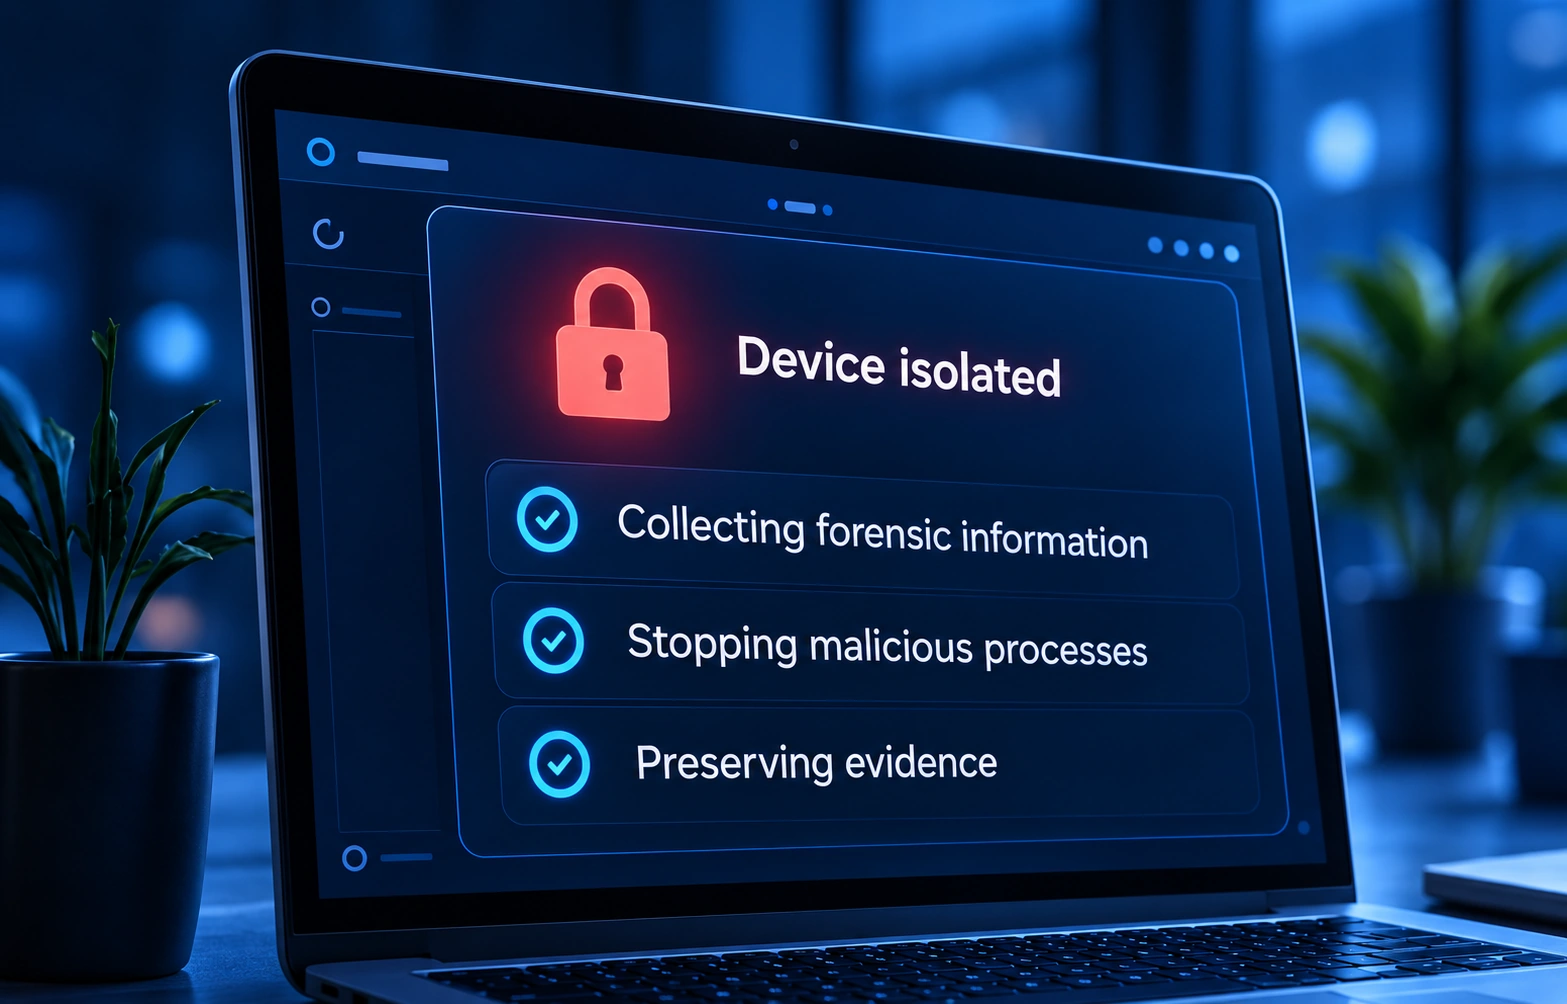
EDR platforms can isolate affected devices, collect forensic information, stop malicious processes and support investigation. The technology is only valuable if alerts are reviewed and acted on. A clear response process defines who investigates, when to isolate, how to preserve evidence and when to escalate.

Photo of laptop showing red padlock Device isolated and forensic actions

05EDR works best with wider controls

Endpoint visibility should be combined with patching, MFA, least privilege, email security, tested backups and security awareness training. CyberXperts.ai helps UK organisations deploy and operate endpoint detection and response as part of a practical security programme.

Patching

MFA

Email security

Security awareness training

Tested backups

Least privilege

GET IN TOUCH

Start with a clear conversation.

Tell us what you want to protect and where you need support.

Please do not include passwords or sensitive information.Privacy Policy

Enquiry update